RESEARCH PAPER
Vehicle ECU On-Board Diagnostic system Threat Analysis and Risk Assessment
1
Faculty of Transport and Aviation Engineering,, Silesian University of Technology, Poland
2
Faculty of Transport and Aviation Engineering, Silesian University of Technology, Poland
These authors had equal contribution to this work
A – Conceptualization; B – Methodology; C – Software; D – Validation; E – Formal analysis; F – Investigation; G – Resources; H – Data curation; I – Writing – original draft; J – Writing – review & editing; K – Visualization; L – Supervision; M – Project administration; N – Funding acquisition
Submission date: 2026-01-12
Final revision date: 2026-05-30
Acceptance date: 2026-10-02
Online publication date: 2026-10-30
Corresponding author
Piotr Pełechaty
Faculty of Transport and Aviation Engineering,, Silesian University of Technology, Krasińskiego, 40-019, Katowice, Poland
Faculty of Transport and Aviation Engineering,, Silesian University of Technology, Krasińskiego, 40-019, Katowice, Poland
KEYWORDS
TOPICS
ABSTRACT
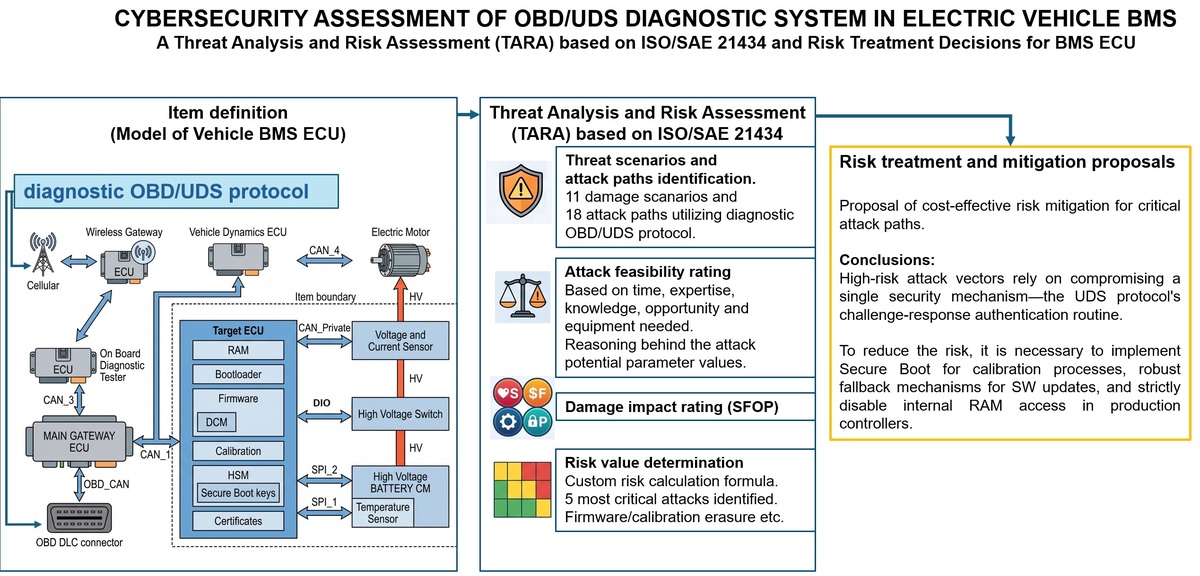
This article presents a security assessment of the on-board diagnostic (OBD) system integrated into a vehicle's electronic control unit (ECU), specifically targeting the Unified Diagnostic Services (UDS) protocol. The research focuses on a representative Battery Management System (BMS) ECU for electric vehicles within its operational context. The study aims to evaluate security vulnerabilities across all OBD functionalities and propose risk mitigation strategies for software implementation. A Threat Analysis and Risk Assessment (TARA) was conducted following the ISO/SAE 21434 standard for road vehicle cybersecurity engineering. The authors identified seven primary assets requiring protection and defined 11 damage scenarios. Furthermore, feasibility ratings were calculated for 18 attack paths involving both physical and wireless OBD interfaces. Based on the assessment, the authors recommend specific software enhancements to mitigate the identified cybersecurity threats.
REFERENCES (30)
1.
International Organization for Standardization. ISO 15031-3:2023 Road vehicles — Communication between vehicle and external equipment for emissions-related diagnostics — Part 3: Diagnostic connector and related electrical circuits: Specification and use. Geneva: International Organization for Standardization; 2023.
2.
International Organization for Standardization. ISO 15031-5:2015 Road vehicles — Communication between vehicle and external equipment for emissions-related diagnostics — Part 5: Emissions-related diagnostic services. Geneva: International Organization for Standardization; 2015.
3.
International Organization for Standardization. ISO 14229-1:2020 Road vehicles — Unified diagnostic services (UDS) — Part 1: Application layer. Geneva: International Organization for Standardization; 2020.
4.
Huang J, Nan J, Chai Z, Lin C. Analysis of UDS diagnostic service applied on vehicle ecu. Applied Mechanics and Materials 2013; 437: 779-782. https://doi.org/10.4028/www.sc....
5.
Zhang Y, Ge B, Li X, Shi B, Li B. Controlling a car through OBD injection. In: 2016 IEEE 3rd International Conference on Cyber Security and Cloud Computing (CSCloud). IEEE; 2016. p. 26-29. https://doi.org/10.1109/CSClou....
6.
Kang TU, Song HM, Jeong S, Kim HK. Automated reverse engineering and attack for CAN using OBD-II. In: 2018 IEEE 88th Vehicular Technology Conference (VTC-Fall); Chicago, IL. IEEE; 2018. p. 1-7. https://doi.org/10.1109/VTCFal....
7.
EVITA Consortium. Deliverable D2.3: Security requirements for automotive on-board networks based on dark-side scenarios. E-Safety Vehicle Intrusion Protected Applications (EVITA); 2009. http://www.evita-project.org/ [accessed 1 May 2026].
8.
European Union Agency for Cybersecurity (ENISA). ENISA good practices for security of smart cars. European Union Agency for Cybersecurity; 2019. https://www.enisa.europa.eu/pu... [accessed 1 May 2026].
9.
United Nations Economic Commission for Europe (UNECE). UN Regulation No. 155 — Uniform provisions concerning the approval of vehicles with regards to cyber security and cyber security management system. Geneva: United Nations; 2021.
10.
European Union. Regulation (EU) 2018/858 of the European Parliament and of the Council of 30 May 2018 on the approval and market surveillance of motor vehicles and their trailers, and of systems, components and separate technical units intended for such vehicles. Official Journal of the European Union 2018; L 151: 1-218.
11.
International Organization for Standardization. ISO 15765-4:2021 Road vehicles — Diagnostic communication over Controller Area Network (DoCAN) — Part 4: Requirements for emissions-related systems. Geneva: International Organization for Standardization; 2021.
12.
International Organization for Standardization. ISO/SAE 21434:2021 Road vehicles — Cybersecurity engineering. Geneva: International Organization for Standardization; 2021.
13.
HEAVENS Consortium. Deliverable D2: Security models. HEAling Vulnerabilities to ENhance Software Security and Safety (HEAVENS). Autosec; 2016. https://autosec.se/wp-content/... [accessed 1 May 2026].
14.
Lautenbach A, Almgren M, Olovsson T. Proposing HEAVENS 2.0 – an automotive risk assessment model. In: Proceedings of the 5th ACM Computer Science in Cars Symposium (CSCS '21). New York, NY: Association for Computing Machinery; 2021. p. 1-12. https://doi.org/10.1145/348890....
15.
Rathore RS, Hewage C, Kaiwartya O, Lloret J. In-vehicle communication cyber security: challenges and solutions. Sensors 2022; 22(17): 6679. https://doi.org/10.3390/s22176....
16.
AUTOSAR GbR. Specification of diagnostic communication manager (AUTOSAR CP R19-11). Munich: AUTOSAR GbR; 2019. https://www.autosar.org/filead... [accessed 22 April 2026].
17.
Kruk T. Practical modelling of threats to ICT systems using the STRIDE model. Pomiary Automatyka Robotyka 2024; 28(2): 93-99. https://doi.org/10.14313/PAR_2....
18.
International Organization for Standardization, International Electrotechnical Commission. ISO/IEC 18045:2022 Information security, cybersecurity and privacy protection — Evaluation criteria for IT security — Methodology for IT security evaluation. 3rd ed. Geneva: International Organization for Standardization; 2022.
19.
Pandey S, Grover J, Rai R. Decoding in-vehicle communications: analyzing CAN bus data for enhanced security. SN Computer Science 2025; 6: 889. https://doi.org/10.1007/s42979....
20.
Marchetti M, Stabili D. Anomaly detection of CAN bus messages through analysis of ID sequences. In: Proceedings of the 2017 IEEE Intelligent Vehicles Symposium (IV). IEEE; 2017. p. 1577-1583.
21.
Kumar R, Sahu H, Penta A, Bhatt P. Reverse engineering of CAN (Controller Area Network) of an electric vehicle. In: Proceedings of the Symposium on International Automotive Technology (SIAT); Pune, India. SAE International; 2026. https://doi.org/10.4271/2026-2....
22.
Pełechaty P, Konieczny Ł. Analysis of security vulnerabilities in vehicle on-board diagnostic systems. Diagnostyka 2024; 25(3): 192162. https://doi.org/10.29354/diag/....
23.
Lauser T, Munoz Molto G, Krauß C. (Un)authenticated diagnostic services: a practical evaluation of vulnerabilities in the UDS authentication service. In: Proceedings of the 2024 Cyber Security in CarS Workshop; 2024.
24.
Pareja R, Córdoba S. Fault injection on automotive diagnostic protocols: bypassing the security of protected UDS implementations (Report 3124-1747.EN). USA: Keysight Technologies; 2024.
25.
Matsubayashi M, Koyama T, Okano Y, Tanaka M, Miyajima A, Oshima Y, Ukai S, Wakatsuki T, Sugashima T, Nakamura T. Attacks against UDS on DoIP by exploiting diagnostic communications and their countermeasures. In: 2021 IEEE 93rd Vehicular Technology Conference (VTC2021-Spring). IEEE; 2021. p. 1-6. https://doi.org/10.1109/VTC202....
26.
Green C, Chatterjee R, Daily J. Exploiting diagnostic protocol vulnerabilities on embedded networks in commercial vehicles. In: Proceedings of the Symposium on Vehicle Security and Privacy (VehicleSec); San Diego, CA. San Diego: Internet Society; 2024. https://doi.org/10.14722/vehic....
27.
Lauser T, Krauß C. Formal security analysis of vehicle diagnostic protocols. In: Proceedings of the 18th International Conference on Availability, Reliability and Security (ARES 2023). New York, NY: Association for Computing Machinery; 2023. p. 1-10. https://doi.org/10.1145/360016....
28.
Rohith M, Sreelakshmi K. Design and integration of gateway electronic control unit (ECU) for automotive electronics applications. In: 2021 Asian Conference on Innovation in Technology (ASIANCON); Pune, India. IEEE; 2021. p. 1-4. https://doi.org/10.1109/ASIANC....
29.
Robert Bosch GmbH. The E/E architecture of the future (Whitepaper). Bosch Mobility; 2023. https://www.bosch-mobility.com... [accessed 18 May 2026].
30.
Vector Informatik GmbH. OBDonUDS - SAE J1979-2. Vector Informatik GmbH; 2023. https://www.vector.com/int/en/... [accessed 18 April 2026].
Share
RELATED ARTICLE
| eISSN: | 2956-3860 |
| ISSN: | 1507-2711 |
We process personal data collected when visiting the website. The function of obtaining information about users and their behavior is carried out by voluntarily entered information in forms and saving cookies in end devices. Data, including cookies, are used to provide services, improve the user experience and to analyze the traffic in accordance with the Privacy policy. Data are also collected and processed by Google Analytics tool (more).
You can change cookies settings in your browser. Restricted use of cookies in the browser configuration may affect some functionalities of the website.
You can change cookies settings in your browser. Restricted use of cookies in the browser configuration may affect some functionalities of the website.